vRisk Solution

Information Asset Management

Maintain visibility of important information assets within your wider risk and governance framework.

Information is a critical organisational asset. vRisk includes Information Assets as part of its broader risk management platform, allowing organisations to maintain information-asset records alongside audits, incidents, documents, sites, risk profiles and reporting.

Information asset registersInformation-governance reviewsInformation-security audits
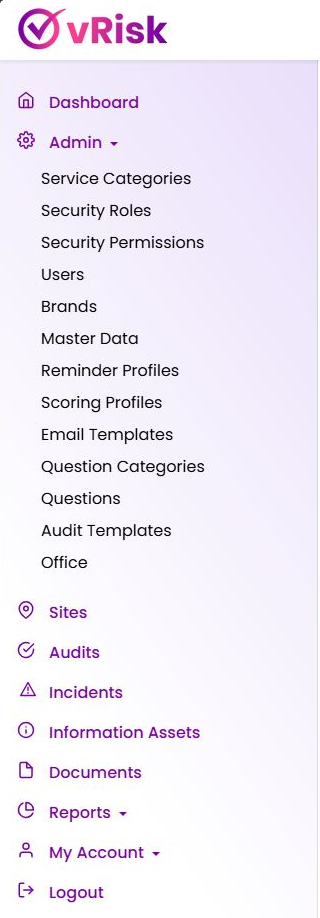
vRisk navigation showing audits, incidents, information assets, documents and reports
Configurable audit engineBuild your own questions and reusable templates.
P×S
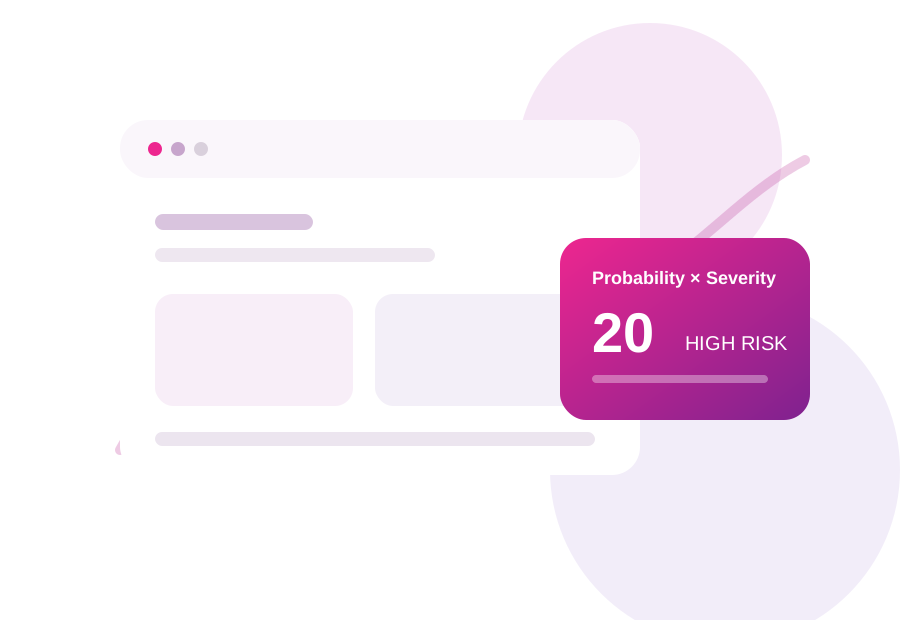
Consistent risk scoringProbability × Severity
The challenge

Bring information governance into the wider risk picture

Information asset registers can become isolated spreadsheets that are difficult to maintain and disconnected from wider governance activity. vRisk provides a dedicated Information Assets area within the same system used for organisational audits and risk management.

  • Replace disconnected spreadsheets and documents with structured audit data.
  • Use a repeatable scoring method across sites, teams and audit types.
  • Keep audit, incident and governance information within one risk environment.
Built around your organisation

One framework, configured to your requirements

vRisk is not a fixed checklist. Administrators maintain the question library, build templates and apply a common risk approach across different assurance activities.

Maintain a central information-asset viewRecord important information assets in a dedicated area of vRisk.
Connect information assets with organisational riskKeep information-governance activity within the same broader risk environment.
Use audits to review information controlsCreate configurable audit templates for information-security, data-handling or…
Keep supporting documents togetherUse the documents functionality alongside information assets and audits.
How vRisk helps

A practical platform for audit, risk and assurance

Configure the content around your organisation while keeping the process consistent for the people completing and reviewing audits.

1

Maintain a central information-asset view

Record important information assets in a dedicated area of vRisk.
2

Connect information assets with organisational risk

Keep information-governance activity within the same broader risk environment.

3

Use audits to review information controls

Create configurable audit templates for information-security, data-handling or governance processes.

4

Keep supporting documents together

Use the documents functionality alongside information assets and audits.

5

Support wider management oversight

Use sites, reports, roles and permissions as part of the overall governance framework.

Typical use cases

Use the same audit framework to assess information risk

Because vRisk audit templates are configurable, organisations can create questions around information handling, ownership, controls and internal processes, then assess relevant responses using the same Probability × Severity framework used elsewhere in the organisation.

Information asset registers
Information-governance reviews
Information-security audits
Data-handling audits
Department information reviews
Business-process information audits
Internal control assessments
Supplier information-risk reviews
Document-governance processes
Periodic information-asset reviews
Probability × Severity

Turn findings into measurable, prioritised risk

vRisk uses a straightforward Probability × Severity approach for relevant responses. The matrix gives teams a shared language for comparing findings and helps management focus attention where risk is highest.

  • Simple to explain to auditors, site teams and management.
  • Consistent scoring supports comparison across recurring audits.
  • Risk profiles can use scored findings to provide a wider organisational view.
Probability
5
5
10
15
20
25
4
4
8
12
16
20
3
3
6
9
12
15
2
2
4
6
8
10
1
1
2
3
4
5
1
2
3
4
5
Severity
LowModerateHighCritical
Audit to action

Build → Audit → Assess → Act → Improve

A repeatable workflow makes assurance easier to run and easier to explain.
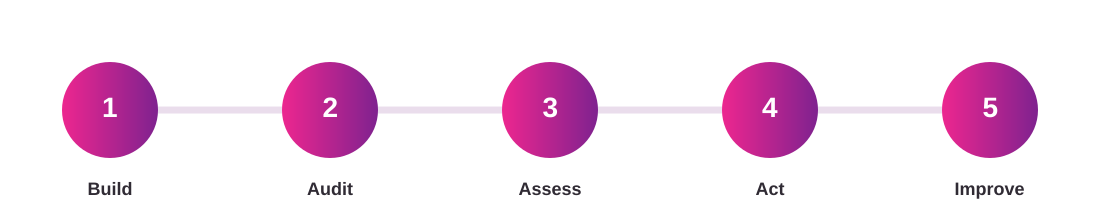
Five-step vRisk workflow: Build, Audit, Assess, Act, Improve
Actual vRisk product navigation
One central platform

Beyond the audit

vRisk brings related risk and governance information into the same environment, reducing the need for separate spreadsheets and disconnected repositories.

Auditsbuild information governance and information-risk reviews.
Risk Profilessupport a broader view of organisational risk.
Incidentsmaintain incident records within the same environment.
Documentsmanage relevant documents alongside information assets.
Security Roles and Permissionscontrol access within the platform.

Product screenshot shown from the current vRisk interface.

Who vRisk is for

Designed for the people responsible for risk, safety, assurance and operations

Information Governance ManagersRisk ManagersCompliance ManagersIT ManagersData Protection and Governance TeamsInternal Audit TeamsOperations ManagersSenior Management
Book a practical demonstration

Make information assets part of your organisational risk framework

Book a vRisk demonstration to see how information assets can be managed alongside audits, incidents and wider risk information.

Bring one of your current checklists, audits or risk processes.
See how your own questions can become a reusable vRisk template.
Explore how Probability × Severity and wider vRisk modules fit your process.
CAPTCHA Image
Preview only: the form layout and validation are working. Connect the POST action to your CRM/email/API endpoint before publishing.
Frequently asked questions

Questions about Information Asset Management

Does vRisk include an information asset register?

vRisk includes a dedicated Information Assets area for maintaining organisational information-asset records.

Can we audit information-security or data-handling processes?

Yes. Administrators can create questions and audit templates for information-related controls and processes.

Can information risk use the same scoring approach as other audits?

vRisk’s audit framework is built around Probability × Severity for assessing relevant responses.

Is document management included as well?

Yes. Documents are another part of the wider vRisk platform.